
🤝 Top Collaborators


🤓 Latest Submissions
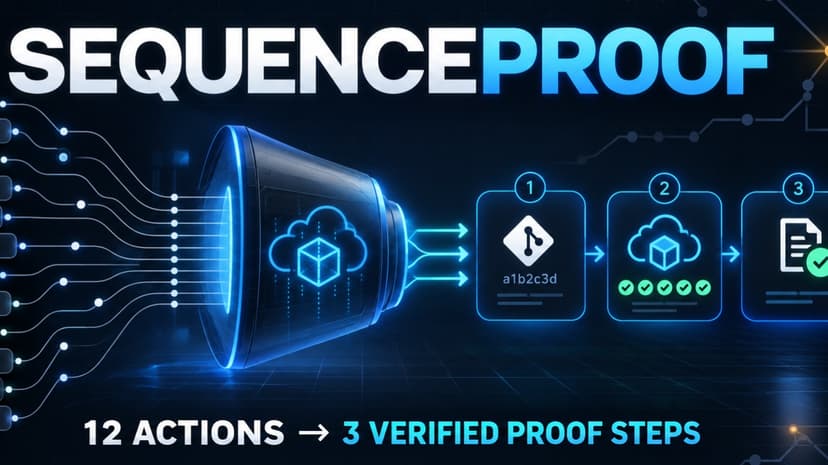
SequenceProof: Turn Bug Traces Into Proof
A bug report can be technically correct and still leave a developer hunting through a dozen unrelated steps. Stateful failures are especially painful: account switches, cached permissions, session changes, and background actions can make the real trigger almost impossible to see. SequenceProof turns that noisy trace into a compact, executable proof. The developer provides a public GitHub repository, an immutable commit SHA, and a reproducing action trace. The repository opts in through a small SequenceProof manifest that defines how its trace should be executed. SequenceProof then creates a disposable Daytona sandbox, checks out the exact commit, runs the original trace, and learns the precise failure ID. Its reduction engine tests smaller candidate traces from fresh repository state. A candidate is accepted only when it reproduces the same failure ID. Execution errors, invalid traces, and unrelated failures are rejected. The final trace is replayed five independent times, the corrected implementation is tested separately, and a bounded one-minimal certificate confirms that removing any single retained step breaks the reproduction. Our live demonstration starts with 12 actions surrounding a stale authorization bug. SequenceProof reduces them to three actions: switch to an admin account, switch to a viewer account, and attempt to read a protected report. All five confirmation runs reproduce STALE_ROLE_AUTHORIZATION with separate run IDs. The corrected implementation returns NOT_REPRODUCED. The browser interface shows the real backend phases, candidate executions, trace hashes, confirmation runs, fixed-path result, and cleanup status. Developers can download the complete JSON evidence for an issue, pull request, or debugging handoff. After every job, the disposable sandbox is destroyed and its deletion is independently verified. SequenceProof is built for developers, QA engineers, maintainers, and teams debugging failures that depend on action order and hidden state. It replaces a vague reproduction story with a short sequence that another engineer can execute, inspect, and trust.
27 Sep 2026

ReproForge Sentinel — Claim-to-Evidence AI
AI systems can generate benchmark claims, model promises, and technical demonstrations faster than teams can verify them. ReproForge Sentinel closes that trust gap by turning an AI/ML claim into structured, inspectable evidence. A user submits a repository URL, the exact claim, a runtime target, and declared security policies. ReproForge evaluates the available claim metadata and policy signals, applies deterministic ShadowGuard risk and reproducibility scoring, records a trace of the evaluation, and produces a Reproducibility Passport. The Passport contains the verdict, evidence chain, missing proof, blocked actions, integrity hashes, security notes, and exportable JSON/PDF results. The hackathon build combines a premium React and TanStack interface with a FastAPI backend, Docker packaging, tests, proof schemas, and AMD/Gemma integration adapters. It also includes an AMD ROCm capture workflow that accepts hardware evidence only when device identity, HIP/ROCm, AMD SMI telemetry, workload metrics, and artifact hashes are successfully captured. Our guided sample is clearly labeled and designed for a reliable judge walkthrough. The current public MVP evaluates submitted claim metadata and declared policies; it does not yet clone or execute arbitrary repositories. Real Fireworks/Gemma inference and direct AMD ROCm telemetry remain explicitly marked pending when verified runtime provenance is unavailable. ReproForge never replaces missing measurements with invented proof. ReproForge is not a “truth machine.” It is an evidence machine: a verification layer for AI teams, security reviewers, researchers, investors, and judges who need to understand what was checked, what passed, what failed, and what still cannot be proven.
13 Jul 2026

