🤝 Top Collaborators
🤓 Latest Submissions
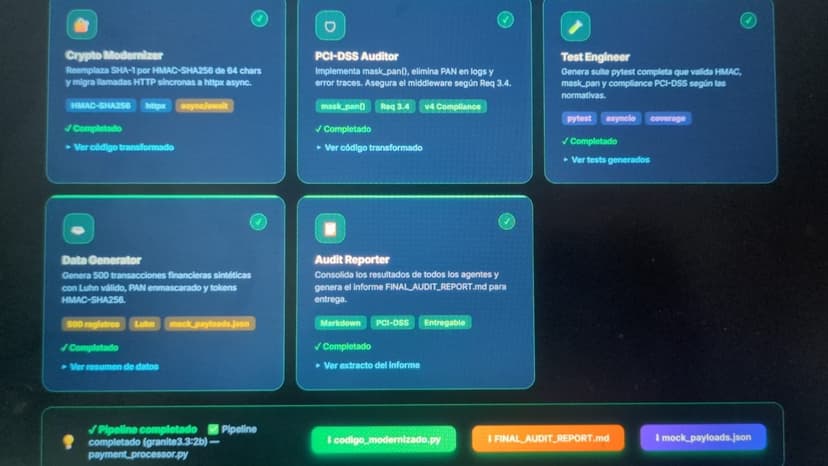
AMCE: Autonomous Modernization Engine
Adapting legacy systems to strict security regulations, such as PCI-DSS v4.0, is a critical bottleneck in enterprise engineering. Traditionally, development teams spend weeks on manual auditing, reviewing code lines to locate outdated dependencies, security breaches, or poor logging practices. This process is not only inefficient and costly, but it is also highly prone to human error, leaving undetected security gaps, weak encryption, and exposed personally identifiable information (PII) that can lead to severe fines and CI/CD deployment blocks.
Hackathon link
27 Sep 2026
