🤝 Top Collaborators


🤓 Latest Submissions
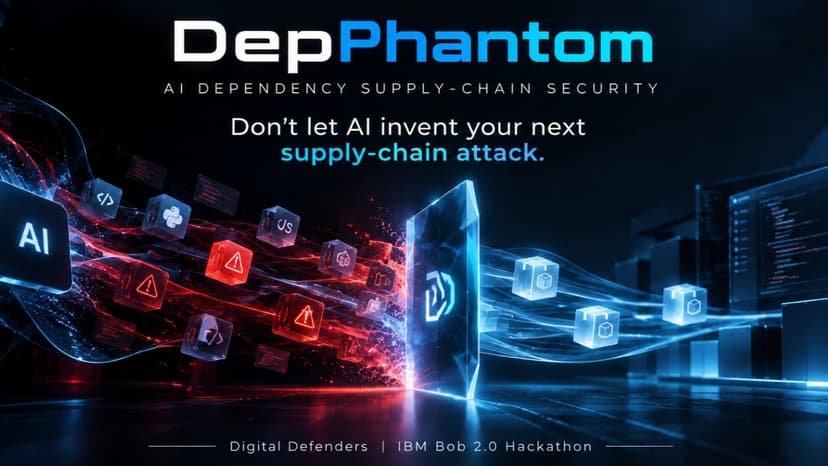
DepPhantom: AI Dependency Supply-Chain Security
AI coding agents are evolving from code-generation assistants into autonomous software engineers capable of selecting libraries and executing package installation commands. This introduces a new software supply-chain attack surface: AI-generated dependency hallucinations. Large Language Models can generate plausible package names that do not actually exist. Attackers can exploit this behavior by registering malicious packages under hallucinated names or creating typosquatting packages that closely resemble trusted libraries. If an autonomous agent executes npm install or pip install without sufficient verification, untrusted code can enter the development or CI/CD environment before traditional security controls respond. Existing Software Composition Analysis (SCA) and dependency scanners primarily focus on vulnerabilities in dependencies that have already entered the environment. The missing security boundary is the decision that occurs before installation: should this AI-generated dependency be trusted at all? DepPhantom addresses this gap by introducing a pre-installation security gateway between autonomous AI coding agents and package installation. When an AI agent requests a dependency, DepPhantom performs multi-signal verification before allowing installation. It analyzes registry identity, package-name similarity, typosquatting indicators, package metadata, installation behavior, dependency relationships, and AI intent alignment. For example, if an AI agent requests requets while attempting to implement HTTP functionality, DepPhantom can detect its strong similarity to the legitimate requests package and identify it as a potential hallucination or typosquatting risk. These security signals are processed through an explainable risk engine that generates one of three actionable decisions: ALLOW · REVIEW · BLOCK Rather than presenting only an opaque risk score, DepPhantom exposes the evidence behind each decision, enabling developers and security teams to understand why a dependency was trusted, flagged, or blocked. The platform also provides dependency analysis reports, security event logging, policy controls, audit trails, and deterministic attack demonstrations, with support for package ecosystems such as PyPI and npm. DepPhantom is designed for developers, DevSecOps teams, security engineers, and organizations adopting autonomous coding agents. Its key innovation is the AI-to-package trust boundary. Traditional dependency security asks, "Is this installed package vulnerable?" DepPhantom asks an earlier question: "Should this AI-generated dependency be trusted and allowed into the environment in the first place?" By intercepting dependency decisions before installation, DepPhantom shifts software supply-chain security from post-installation detection toward pre-installation prevention.
27 Sep 2026
