🤝 Top Collaborators

🤓 Latest Submissions
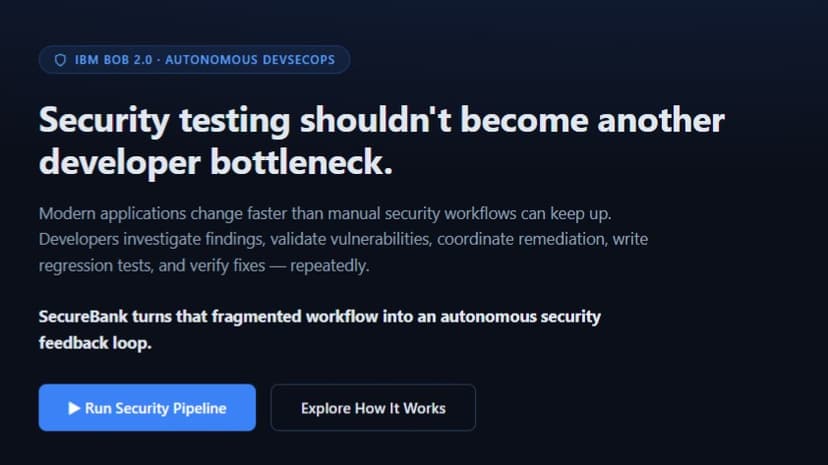
Autonomous DevSecOps Pipeline (bob-the-fixer)
Problem & Challenge: Modern application development cycles run faster than traditional security workflows can keep up. Security testing today is heavily fragmented, relying on disconnected manual activities: scanning, manual exploit reproduction, false-positive filtering, CVSS risk scoring, manual code patching, writing regression test cases, and post-fix re-testing. This fragmentation introduces severe context switching, developer friction, release bottlenecks, and inconsistent security validation. Solution: SecureBank redefines application security by transforming manual security testing into a continuous, autonomous, evidence-backed DevSecOps feedback loop powered by IBM Bob. Instead of developers coordinating disparate security tools and manually patching bugs, our closed-loop 7-stage multi-agent pipeline orchestrates the complete vulnerability lifecycle autonomously: 1. Recon Agent: Discovers target endpoints, API specifications, and live application attack surfaces. 2. Red Team Engine: Simulates real-world attack vectors including IDOR, SQL Injection, XSS, Arbitrary File Upload, and Privilege Escalation. 3. Security Judge: Independently replays exploit payloads to confirm findings and eliminate false positives. 4. Risk Analyzer: Computes CVSS vector scores, calculates blast radius, and prioritizes actionable findings. 5. Blue Team Patch Agent: Generates precise source code remediations and auto-compiles PyTest regression test suites. 6. Verification Engine: Re-tests original exploit payloads and verifies legitimate traffic health to ensure zero application regressions. 7. Adaptive Red Team: Executes bypass variations to validate defense boundaries against secondary exploits. Target Users & Interaction: Our primary target users are DevSecOps engineers, security teams, and full-stack software developers. Users interact through an intuitive control center dashboard (or CI/CD pipeline hook) where they trigger automated runs, observe live stage execution, inspect tamper-proof JSON evidence chains, and review auto-generated regression test suites. Creativity & Uniqueness: What sets SecureBank apart is its adversarial closed-loop architecture. Rather than relying on static security scanners or isolated LLM codegen, SecureBank pairs offensive Red Team agents against defensive Blue Team patch agents with an independent Security Judge ensuring complete validation accuracy without human intervention. Effectiveness & Efficiency: By eliminating manual handoffs, false positives, and patch verification cycles, SecureBank shortens security feedback loops from days to seconds, allowing teams to ship secure code at high velocity.
27 Sep 2026
