🤓 Latest Submissions
BobGuard : Autonomous DevSecOps Orchestrator
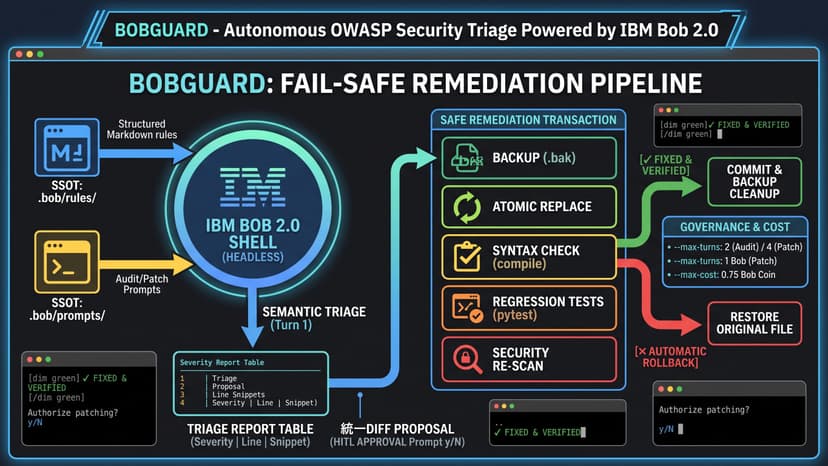
Problem Statement Securing modern web applications against OWASP Top 10 vulnerabilities is heavily bottlenecked by two major flaws in conventional DevSecOps: brittle static scanners that flood teams with false positives, and unverified AI patch generators that hallucinate fixes, introduce syntax errors, or break business logic. Because automated remediation tools lack safety boundaries, engineering teams spend hours manually debugging vulnerabilities and triaging alerts, slowing down release cycles while leaving exploitable flaws in production. The Solution: BobGuard BobGuard is an autonomous DevSecOps orchestrator and interactive CLI agent powered by IBM Bob 2.0 and IBM Granite. It bridges the gap between semantic vulnerability discovery and safe, verified code remediation. Built on a Single Source of Truth (SSOT) architecture, BobGuard derives all audit policies and safe patching guardrails directly from declarative Markdown documents (.bob/rules/ and .bob/prompts/), ensuring synchronized behavior across both headless terminal automation and the IBM Bob IDE Agent. Target Users & User Interaction BobGuard is designed for software engineers, DevSecOps teams, and security analysts maintaining polyglot web repositories. Developers interact with BobGuard directly from their terminal using straightforward commands such as bobguard scan for read-only audits or bobguard run for guided remediation. - Pre-Flight Workspace Guard: Prevents wasted inference credits by validating target directories before invoking the LLM. - Rich Visual Triage: Renders findings in an actionable, color-coded terminal table detailing severity, file locations, line numbers, and evidence. - Human-in-the-Loop (HITL) Governance: Previews colorized unified diffs and demands explicit developer confirmation (y/N) before applying any modifications to the local filesystem. Unlike traditional AI tools that blindly overwrite files, BobGuard enforces an atomic Fail-Safe Remediation Transaction: Backup -> Atomic Patch -> Syntax Check -> Regression Suite -> Security rescan -> Commit/Rollback Effectiveness & Efficiency BobGuard compresses the Mean Time to Remediate (MTTR) from hours of manual work down to seconds of automated execution. By combining LLM-powered semantic taint analysis with multi-stage verification (including native language compilers, test runners like pytest, and targeted security re-scans), BobGuard guarantees that every applied patch is syntactically sound, functionally regression-free, and definitively resolved. It transforms security from a bottleneck into a seamless, trusted, push-button developer experience.
27 Sep 2026

