

Aniket Khuntia@aniket_wnl
1
Events attended
1
Submissions made
India
1 year of experience
About me
🚀 I build AI for real-world impact, from rural healthcare to ocean anomaly detection. I'm Aniket, a Data Science undergrad at VIT Vellore (B.Tech, 2026-2030). I learn by building, turning internships at IBM, ISRO, Google × Kaggle, and IIT Bhubaneswar into deployed projects. 🔥 WHAT I'VE BUILT 🌊 OCEANNOVA | AI Ocean Anomaly Intelligence End-to-end ML pipeline detecting anomalous signatures in NASA PACE hyperspectral data (200+ bands) via PCA + Isolation Forest. Classifies causes with Random Forest. Live Vercel+Plotly demo. 🩺 RuralPulse | Multilingual AI Agent AI platform aiding rural patients across languages to close healthcare access gaps. Built as my Google × Kaggle Gen AI capstone using multi-agent systems. 🧭 Mentauri | AI Career Strategist Gemini-powered strategist mapping Indian opportunities to student skills and simulating career paths. 🏢 EXPERIENCE ▪️ IBM: Data Analytics with AI Intern ▪️ ISRO: Geospatial Data Analysis Intern ▪️ Google × Kaggle: Gen AI Virtual Intern ▪️ IIT Bhubaneswar: Technical Intern (CS, Electrical, Semiconductor) 🛠️ SKILLS Tools: Python · SQL · Java · Pandas · NumPy · scikit-learn · Streamlit · GitHub Domains: Machine Learning · Data Science · AI Agents · Gen AI · Anomaly Detection · Geospatial 🎓 CERTIFICATIONS Azure Data Fundamentals · Deloitte Data Analytics · Gemini Educator · AI Skills Fest '26 · ISRO-IIRS Geospatial · AI Agents Intensive 🤝 CONNECT Actively seeking internships, research, and collaborations in ML and Applied AI. 📩 [email protected] 💻 github.com/dragunxwho13
🤓 Latest Submissions
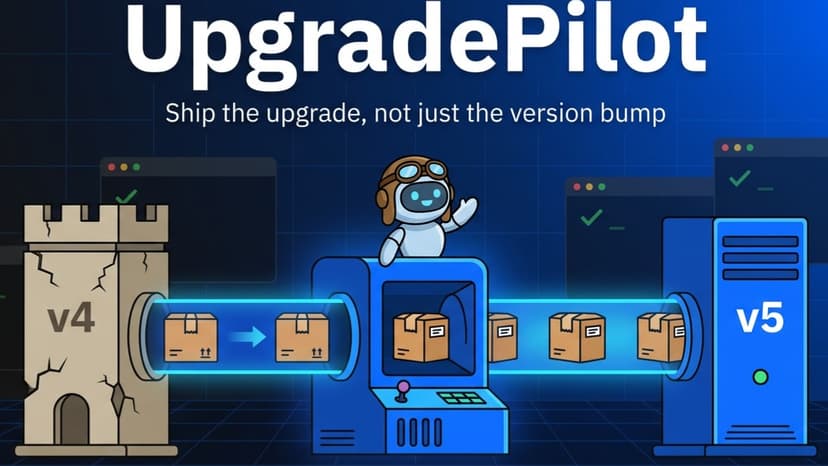
UpgradePilot — Agentic Dependency Upgrade Co-Pilot
Problem Upgrading major-version dependencies (e.g. Express 4→5, Mongoose 6→7, Flask 2→3) is one of the most error-prone and time-consuming tasks in application maintenance. Engineers must manually grep source code for removed APIs, read multiple changelogs, estimate risk, write codemods, bump version pins, run tests, and fix regressions — a process that routinely takes 10–20 hours per project and is prone to missed hits, partial migrations, and broken CI. Solution UpgradePilot is a six-agent CLI pipeline that automates the entire upgrade workflow end-to-end - 1. Scanner — globs all .js/.mjs/.cjs (Node) or .py (Python) source files, matches them line-by-line against a rule database (18 rules × 5 packages with severity weights), and produces a usage map with exact file:line hits and a risk score per rule. 2. Librarian— looks up embedded migration knowledge (Express 5, Mongoose 7, Flask 3, requests) and returns ordered action items and references for each breaking dependency. 3. Planner — builds a risk-scored migration plan using an occurrence × severity × proximity formula, estimates manual vs automated effort, and sorts packages into a safe upgrade order (dev deps first, then prod by ascending risk). 4. Codemod Crew — spawns one worker per package via Promise.all, applies regex-based transforms line-by-line, generates unified diff patches (pure-JS, no external differ), and writes a full replacement log — all without touching source files in dry-run mode. 5. Verifier — in real mode: bumps package.json, runs npm install + npm test, and applies up to 3 targeted fix cycles if tests fail. In dry-run mode: re-scans the codemodded source and asserts zero legacy hits remain. 6. Scribe — renders a Markdown or JSON upgrade report with per-package risk tables, migration steps, effort savings, and rollback instructions. Impact (measured on included sample app) - Node.js pipeline (Express 4→5, Mongoose 6→7): 53 breaking hits found automatically; manual estimate 1,208 min → UpgradePilot 228 min → **81% time saved**; 12/12 tests green on new majors with 0 fix cycles. - Python pipeline (Flask 2→3, requests): 13 breaking hits across 6 rules; 216 min manual → 41 min automated → 81% time saved. Target users : Backend engineers and DevOps teams maintaining multi-year-old Node.js or Python services who need to unblock security patches, EOL migrations, or framework upgrades without dedicating a full sprint to them. What makes it unique: The pipeline is model-agnostic — every agent is designed to delegate its reasoning step to an LLM (IBM watsonx.ai Granite) via a documented injection interface, without changing the exported API. The rule database, risk formula, effort estimates, and codemod transforms are all data-driven from a single `breaking-changes.json` file, making it trivially extensible to new packages and ecosystems.
27 Sep 2026


