🤓 Latest Submissions
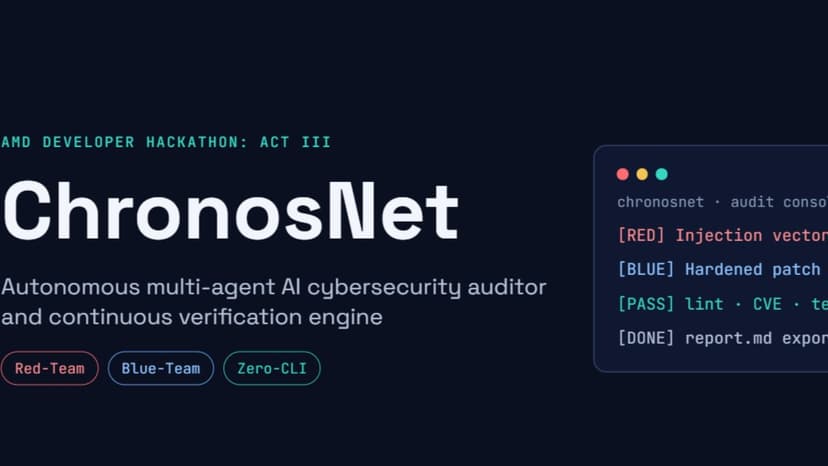
ChronosNetAI
Traditional static application security testing (SAST) often requires navigating fragmented terminal commands (flake8, pip-audit, pytest) and manually interpreting raw security logs. Furthermore, standard single-pass AI coding assistants frequently miss edge-case logic flaws or provide unverified patch suggestions. ChronosNet bridges this gap by delivering a streamlined, zero-CLI web dashboard where developers can inspect entire project repositories or isolated code snippets in seconds. Key Capabilities: 1. Dual-Perspective Multi-Agent AI Debate: Utilizes an offensive Red-Team Agent to identify exploitable attack vectors (SQLi, Command Injection, Logic Flaws) paired with a defensive Blue-Team Agent that synthesizes verified, hardened code rewrites. 2. Dual Project Ingestion: Supports seamless drag-and-drop ingestion of whole project folders (building an interactive file selection tree) alongside a direct copy-paste code buffer for single snippets. 3. Automated Security Pipeline: Executes flake8 (code style/syntax), pip-audit (CVE dependency checks), and pytest (unit testing) directly through the Flask backend without opening a terminal window. 4. Fast Demo Mode vs. Live Engine: Features a presentation-ready instant response toggle for zero-wait demonstrations alongside a live LLM integration mode for deep multi-turn analysis. 5. AMD Acceleration: Engineered to leverage AMD ROCm software stack for accelerated local LLM reasoning and AMD Ryzen multi-core processing for asynchronous background testing. ChronosNet empowers developers and security auditors to continuously verify and harden codebases with zero command-line friction.
18 Oct 2026

