🤓 Latest Submissions
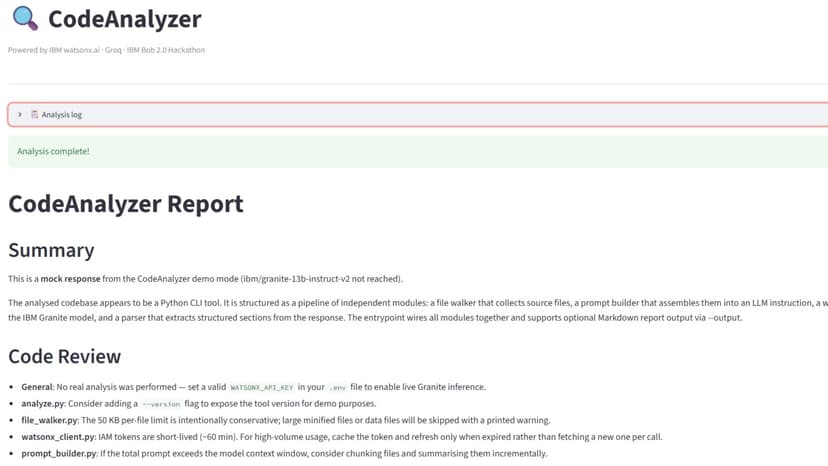
CodeAnalyzer
Problem Statement: Onboarding into unfamiliar codebases, performing manual code reviews, and identifying architectural risks are time-consuming processes prone to human oversight. Developers often lack immediate context on multi-file dependencies, leading to overlooked bugs, non-standard code style, and security vulnerabilities. Solution Overview: CodeAnalyzer is an open-source, automated repository reviewer designed for individual developers, team leads, and open-source maintainers. It combines a clean Streamlit web dashboard with a robust Command Line Interface (CLI) to process local repositories instantly. User Experience & Interaction: Users launch the tool via Streamlit or terminal, select their target local repository directory, and choose their preferred LLM inference provider. CodeAnalyzer traverses the project structure, parses source code files safely, assembles context-aware prompts, and generates structured Markdown reports. The output includes an Executive Architectural Summary alongside actionable, per-file Code Review findings highlighting bugs, refactoring opportunities, and security recommendations. Uniqueness & Innovation: CodeAnalyzer features a platform-agnostic, resilient architecture built for operational reliability. To overcome deployment constraints during hackathons, it includes robust multi-provider fallback logic: while integrated for IBM watsonx.ai, it uses real-time Groq LLM inference as its live engine alongside an automated watsonx mock fallback. Additionally, it handles Windows-specific UTF-8 subprocess encoding seamlessly, ensuring consistent cross-platform performance. Effectiveness & Efficiency: By automating repetitive code inspection tasks, CodeAnalyzer significantly reduces code review turnaround time, accelerates developer onboarding, and maintains high code quality without requiring complex cloud setups.
27 Sep 2026
