🤝 Top Collaborators
🤓 Latest Submissions
AegisDev: Autonomous Software Quality Gate
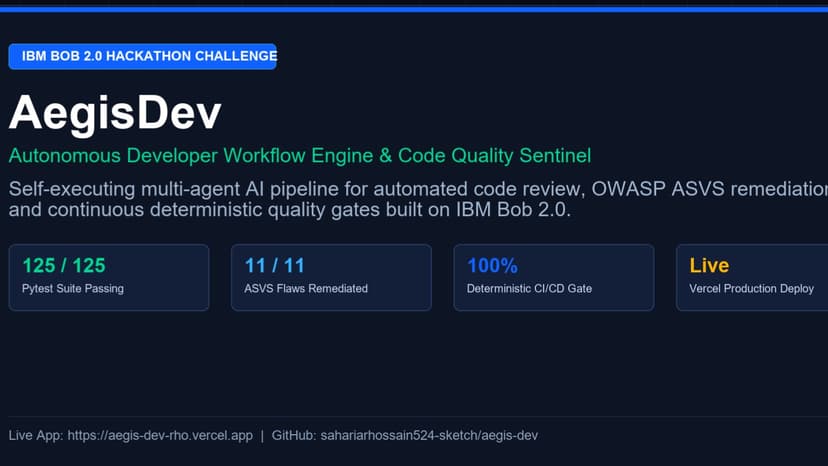
### 1. Problem Statement Modern software engineering teams face three compounding crises: developer cognitive overload from context-switching between feature work and security reviews, slow and fragmented onboarding that delays a new hire's first PR by weeks, and manual code review bottlenecks where critical OWASP vulnerabilities slip through to production. Human reviews are inconsistent, expensive, and slow—creating multi-day PR queues and accumulated technical debt. ### 2. Solution: AegisDev + IBM Bob 2.0 AegisDev is an autonomous developer workflow engine and zero-trust quality gate built natively using IBM Bob 2.0 Agent Mode. Instead of merely surfacing lint warnings, AegisDev autonomously reasons through codebases, identifies security vulnerabilities against the OWASP ASVS 4.0 standard, writes production-ready refactor patches, and engineers comprehensive Pytest regression guardrails wired to GitHub Actions CI/CD. ### 3. Target Users - Software Engineers & Teams seeking to eliminate cognitive toil and automate code reviews. - Engineering Leaders & Tech Leads accelerating developer onboarding and team velocity. - Application Security (AppSec) Teams enforcing rigorous zero-trust compliance across microservices without slowing down releases. ### 4. How Users Interact with AegisDev - Interactive Autonomous Quality Gate: Developers trigger the live quality gate simulation or test endpoints via the interactive Swagger UI and real-time execution dashboard. - Git Push & PR Automation: Developers push code normally; IBM Bob 2.0 autonomous pipelines trigger on commit, performing AST analysis, security scanning, and test validation. - Self-Healing PRs & SARIF Reports: AegisDev generates GitHub Security-compliant SARIF 2.1.0 artifacts and comprehensive markdown audit reports documenting exact remediation steps. ### 5. What Makes AegisDev Creative & Unique Unlike passive linters or superficial AI chatbots, AegisDev: - Autonomously Remediates Flaws: It doesn't just warn; it autonomously fixed 11 critical and high vulnerabilities (TD-01 to TD-11), including CWE-798 (hardcoded secrets), CWE-328 (PBKDF2-HMAC password hashing with 600k iterations), CWE-269 (privilege escalation defense), and CWE-613 (token revocation). - Self-Healing QA Guardrails: It generated 125 automated tests achieving 92% test coverage with 0 failures, ensuring zero future regressions. - Fail-Closed Zero-Trust Architecture: Enforces strict environment boundaries, thread-safe data stores, and sanitized error disclosures with correlation IDs. ### 6. Measurable Impact & Resource Efficiency - 11 / 11 Security Findings Remediated: 100% autonomous resolution verified via SARIF 2.1.0. - 125 / 125 Regression Tests Passing: 100% pass rate enforced by a 4-stage GitHub Actions CI/CD pipeline. - Ultra-Efficient Execution: Completed all 3 full hackathon tasks consuming only 10.96 Bobcoins out of the 40 allocated budget (72.6% efficiency savings). - Production-Ready & Live: Deployed live on Vercel Serverless with sub-second cold starts.
27 Sep 2026


