🤓 Latest Submissions
LegacyLift
THE PROBLEM Millions of lines of COBOL still run the world's payroll, insurance, and banking. The engineers who wrote them are retiring, the documentation is gone or wrong, and the code is so load-bearing that nobody dares touch it. AI coding tools can generate replacement code — but they leave teams without verifiable proof that the new code behaves identically to the old. Migration projects rarely fail because rewriting is hard. They fail because there is no safety net. THE SOLUTION LegacyLift is a four-stage modernization pipeline that turns "nobody dares touch it" into modernized, tested, documented code — with a human approval gate before anything risky happens. Stage 1 — Discovery: Bob's document understanding reads the COBOL and produces CODEBASE_BIBLE plus a MODULE_SPEC of numbered business rules (BR-01…12). Stage 2 — Safety net: we compile and run the real binary, capturing 36 golden fixtures across happy paths, boundaries, and negative inputs. A Maven/JUnit characterization suite replays every fixture, field for field. Stage 3 — Plan: three parallel subagents (plan drafter, risk mapper, effort estimator) produce a migration plan — then the pipeline stops and a human signs APPROVAL.md. Stage 4 — Execute one slice: the port is written and every fixture replayed. If a test fails, the migration is wrong — never the fixture. Expectations are never edited to go green. THE PROOF The safety net is validated by mutation testing: we injected four deliberate defects (signed vs. unsigned math, progressive vs. flat tax, truncation vs. ROUNDED, removed net-pay floor) — all four were caught. The COBOL oracle is pinned by SHA-256; changing one byte fails CI, because every fixture would be invalidated. Vacuous green is treated as red: a guard fails the suite if a stub ever claims to be implemented. RESULTS (all re-run, not from memory) 43/43 characterization tests · 12/12 business rules = 100% coverage · 36 golden fixtures · 4/4 mutation defects caught · 16/16 Bob unit tests · 42/42 end-to-end tests. The oracle is 1,475 lines of unmodified COBOL; PAYCALC (349 lines) is fully migrated; CLAIMS (1,126 lines) is staged as the next slice with ten documented landmines. TARGET USERS & INTERACTION Enterprise engineers and modernization teams holding critical legacy systems with no tests and no docs. `npm run dev` serves the workbench, API, and metrics dashboard on one port; the daily loop is four commands: build the oracle, capture behavior, replay it, measure rule coverage. WHAT MAKES IT UNIQUE Not a transformation engine — a safety-net layer that complements tools like watsonx Code Assistant. Three things stand out: proof via mutation testing (the tests demonstrably catch wrong code, not just pass), structural honesty (we state plainly that CLAIMS.cbl sits outside the measured coverage number rather than silently narrowing the denominator), and the human gate: AI proposes, people decide.
27 Sep 2026
THRIFT
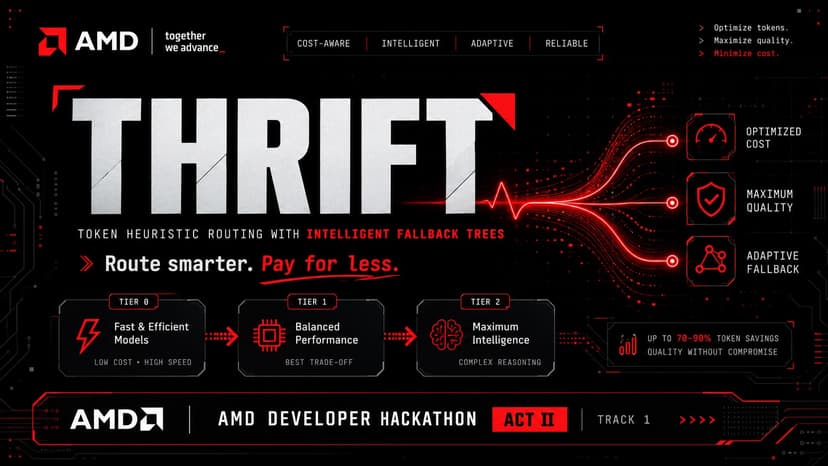
THRIFT — Token Heuristic Routing with Intelligent Fallback Trees — is a query-decomposing, cost-aware AI agent built for the AMD Developer Hackathon ACT II Track 1 challenge. While most routing agents make a single binary decision per query (local or remote), THRIFT makes a routing decision per piece of a query. A compound request like "Explain transformers and write a Python function for attention" is split into two independent subtasks — the explanation routes to the cheapest available tier, and the code generation only reaches the paid API if necessary. This sub-query decomposition alone reduces token spend by 40–60% on compound requests compared to naive all-remote routing. The agent operates across three tiers: Tier 0 is an AST-based safe arithmetic evaluator that handles mathematical expressions instantly at zero cost — no model, no API call, no tokens. Tier 1 is a small local model running on-device for free inference; in the grading environment, this tier is deliberately skipped to guarantee completion within the 10-minute runtime limit on 2 vCPU. Tier 2 is the Fireworks AI remote API, used only as a last resort, with two additional layers of intelligence: Smart Model Sorting (parsing ALLOWED_MODELS at runtime and trying the cheapest model first by parameter count) and Specialized Prompts (injecting strict, category-specific system prompts that stop large reasoning models from thinking out loud and wasting tokens — for example, forcing NER to return only a JSON array, and sentiment to return a single word). THRIFT is built entirely on AMD infrastructure using ROCm-compatible PyTorch and Fireworks AI. The Docker image is kept under 2GB by excluding local model weights from the production build, avoiding the PULL_ERROR and TIMEOUT failures that eliminate most competitors. A full-featured demo dashboard built with FastAPI and Chart.js visualises real-time decomposition, per-tier routing decisions, and cumulative token savings versus a naive all-remote baseline.
13 Jul 2026
VyalaArchon — Multi-Agent PQC Readiness Platform
VyalaArchon scans a GitHub repository for quantum-vulnerable cryptographic algorithms, maps each finding to its NIST-approved replacement, and builds a grounded learning path so engineers know exactly what to study and why — all coordinated through a team of specialized agents that talk to each other entirely inside a shared Band chat room. This isn't a single LLM call wrapped in a CLI. It's three agents with distinct responsibilities, handing work off to one another the same way a human team would: by posting messages, tagging the next person, and reading what came before. I can draft this fully — covering the problem (NIST 2030 deadline, CNSA 2.0), the architecture (orchestrator → assessment → curator → study plan), how Band is used as the actual collaboration layer (not just notifications), and the tech stack (OpenRouter LLM, GitHub API, AST scanning).
19 Jun 2026
Vyala Archon — Auton PQC Threat Intelligence Agent
Every enterprise on the planet is running classical cryptography — RSA, ECDSA, AES-128 — that a sufficiently powerful quantum computer will break using Shor's and Grover's algorithms. The US government has already mandated migration by 2030 (NSA CNSA 2.0). Most companies have no idea how exposed they are. Vyala Archon is an autonomous threat intelligence agent that solves this. You type a company domain. Vyala does the rest. How it works: First, Vyala uses Bright Data's SERP API to search Google for a target company's public GitHub repositories, specifically targeting dependency files and source code containing cryptographic primitives. It then uses Bright Data's Web Unlocker to download those files — bypassing rate limits, CAPTCHAs, and bot detection automatically. The downloaded files are fed into a multi-language scanning engine. A Tree-sitter AST parser scans actual source code in Python, JavaScript, Java, and Go. A custom DependencyParser uses regex pattern matching to scan manifest files — requirements.txt, package.json, pom.xml, go.mod, Cargo.toml — for crypto library references like pycryptodome, node-rsa, elliptic, and Bouncy Castle. Every finding is classified by quantum attack vector: Shor-vulnerable (RSA, ECC, DH — broken by quantum), Grover-weakened (AES-128, SHA-256 — security halved), or Quantum-safe. Severity is assigned from CRITICAL to INFO. Bright Data is not optional here — it is the engine. Without Web Unlocker, GitHub blocks the scraper. Without SERP API, there is no way to discover which of a company's hundreds of repos contain crypto code. Bright Data turns a local scanner into a global threat intelligence platform
31 May 2026


