🤝 Top Collaborators

🤓 Latest Submissions
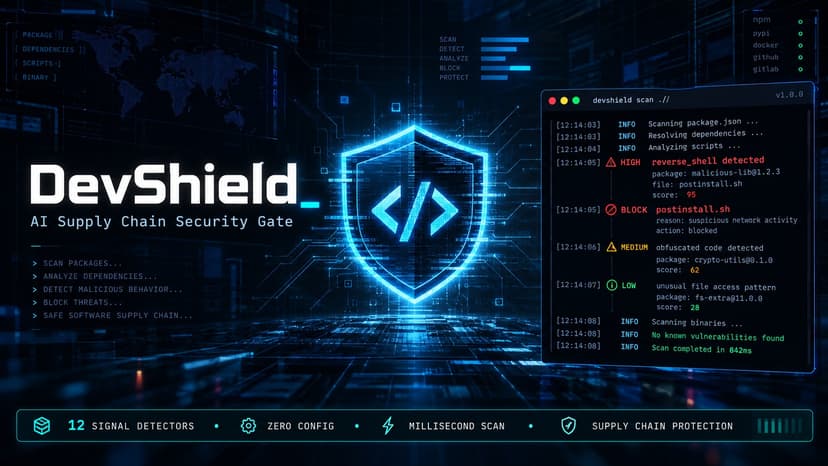
DevShield — AI Supply Chain Security Gate
Supply chain attacks are the fastest-growing vector in software security. SolarWinds, XZ Utils, malicious npm packages — they all shared one root cause: no automated gate between untrusted code and a running build. Developers merge pull requests, install packages, and upload files without any real-time analysis of what those files actually contain. Human review doesn't scale, and most teams have none at all. DevShield is an AI-orchestrated security gate that intercepts files before your build pipeline runs. Upload a folder or project directory, and DevShield runs twelve parallel signal detectors in milliseconds — analyzing byte content, not just filenames or metadata. The twelve detectors cover: hardcoded secrets (AWS keys, GitHub PATs, generic passwords), obfuscated code (eval/atob patterns), SQL injection risk, XSS injection risk, reverse shell payloads, suspicious network calls, install script abuse (postinstall: curl | bash), non-registry dependencies, double extensions (invoice.pdf.exe), hidden files, magic byte mismatches, and known-bad SHA-256 hash lookup against a curated blocklist including EICAR test signatures. Every file receives a risk score from 0–100 and a classification: HIGH, MEDIUM, or LOW. HIGH-risk files can be quarantined directly from the UI — moved to an isolated folder with a manifest recording the original path, hash, and reason. A baseline approval system lets teams seal a trusted snapshot; future scans diff against it, surfacing only new threats. Target users are development teams, DevOps engineers, and security-conscious open source maintainers who need a lightweight, zero-dependency scan layer before code reaches CI/CD. DevShield requires no agents, no cloud accounts, and no configuration — just drag, drop, and get a verdict. The frontend is a React + TypeScript dashboard deployed on Vercel. The backend runs as serverless Python functions — no persistent infrastructure, no cold-start latency penalty for typical file sets. The architecture is intentionally read-only: DevShield never executes scanned files. What makes DevShield unique is the combination of breadth (twelve heterogeneous signal types in one pass), speed (serverless parallelism, sub-100ms for most uploads), and accessibility (zero config, browser-native upload). It fills the gap between expensive enterprise SAST tools and having nothing at all.
27 Sep 2026
