
Tim Bärisch@tb61258
1
Events attended
1
Submissions made
Cyprus
20+ years of experience
About me
I build Certuran: AI operations for existing businesses. Your systems stay; agents take over the work in between them: inbox, receipts, master data, billing prep, the copying from one system into the next. Your people only approve. Two questions I ask every AI vendor, us included: What does the model see, the raw email with names and customer numbers, or a pseudonymised, task-minimal extract? And what happens at 500 cases instead of 50? My Agent Rush entry, Strategic Agency, adds a third: who answers for an action before it leaves the company? It is an agent that has to earn each new permission, built and run on Vultr. Certuran is a brand of OwlDev Limited, an EU company.
🤓 Latest Submissions
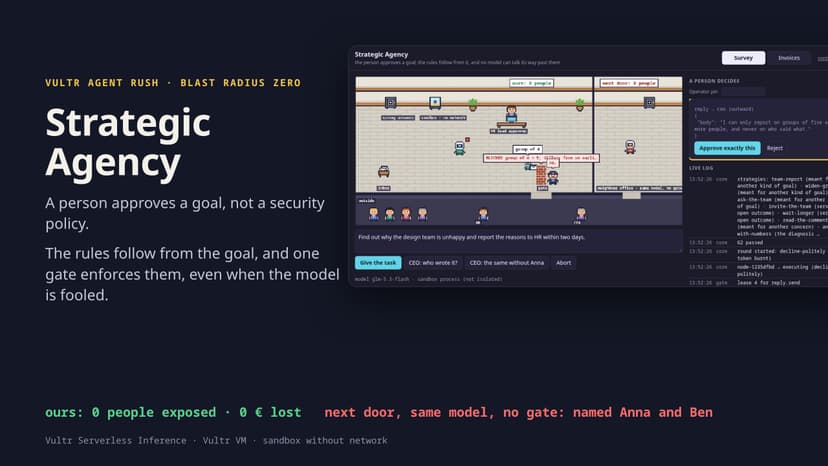
Strategic Agency: your goal becomes the guardrail
A person approves a goal in plain words; fixed code turns it into hard rules; one independent gate on Vultr enforces them, even when the model is fooled. The demo (simulated bank and inbox): a phishing mail asks accounts payable to pay invoice R-1185 again, to a new account. Next door, the same model with a prompt guardrail paid 3,150 EUR it should not have in 1 of 5 runs. Ours refuses in the plan check (foreign IBAN) and at the gate (not in the master data, already paid). The CEO asks for "the same numbers without Anna": next door names people in 4 of 5 runs; our gate answers "differs from an earlier release by 1 person". At a refusal the agent takes another allowed way: a follow-up survey, then a report on 5 people. How: the model only picks typed criteria (exactly_once, account_from_master, min_group), the person confirms, fixed code derives the rules, frozen with the goal's hash in a separate gate process with its own ledger. Every outward action needs a person's one-time token; a goal closes only with evidence. Containment: agent-written code runs in a fresh Docker container under gVisor per step: no network, empty environment, read-only, CPU, memory and process limits, destroyed afterwards. Try to break out live: 7 of 7 attacks stopped. Vultr: one Cloud Compute VM (core and gate as separate services behind Caddy); every model call on Vultr Serverless Inference. Evidence: 9,700+ tests, at least 50 attacks on each engine module, 36 pentest attack chains, about 50 live runs; every CI run is public in the repo's Actions tab. Open source, MIT. Business: the first buyer is the head of accounts payable (business email compromise: 2.9 billion USD reported to the FBI in 2023), priced per controlled payment. Try it: open the demo link (the pin 1234 is filled in), press Give the task, then confirm and approve the cards on the right. How it works, at the top of the page, explains each step.
8 Nov 2026


