🤝 Top Collaborators


🤓 Latest Submissions
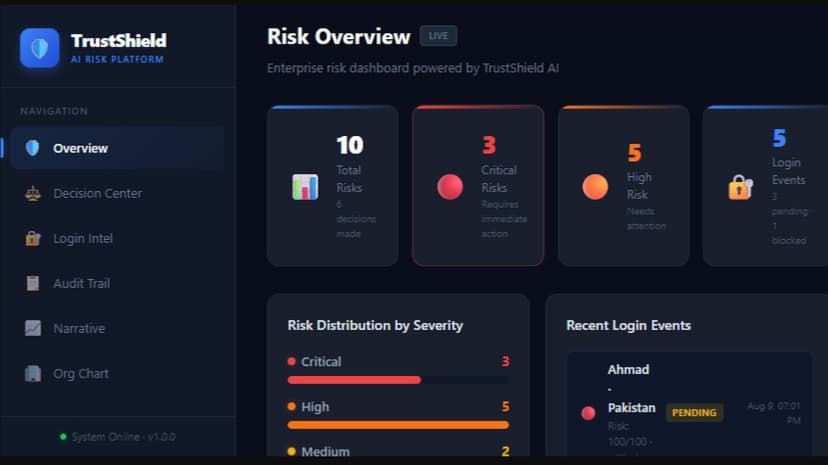
TrustShield
**TrustShield AI** is an explainable and accountable AI governance layer for cybersecurity. It addresses a critical gap in AI-powered security systems: they can detect threats and make decisions, but often fail to clearly explain why a decision was made, what evidence supports it, and when human oversight is required. Our MVP focuses on **suspicious login detection**. TrustShield analyzes signals such as unknown devices, suspicious IP reputation, failed login attempts, unusual locations, and unusual login times. It generates a risk score, confidence level, supporting evidence, and a human-readable explanation. The decision then passes through an **Accountability Engine** that determines whether AI can act autonomously: • Low Risk → Automatically Allow • Medium Risk → Analyst Review • High Risk → Human Approval Required • Low Confidence → Escalate to Human For high-risk events, AI cannot directly execute the recommended action. A security analyst can **Approve, Reject, or Escalate** the recommendation. Every decision is recorded in a complete audit trail, including the security event, AI analysis, evidence, explanation, accountability policy, human action, and final outcome. ### Core Workflow **DETECT → EXPLAIN → EVIDENCE → GOVERN → HUMAN CONTROL → AUDIT** What makes TrustShield different is that it focuses on **what happens after AI makes a cybersecurity decision**. Instead of simply saying "AI detected a threat," TrustShield shows why the AI made the decision, what evidence supports it, how confident it is, what policy governs the action, whether human approval is required, and what ultimately happened. TrustShield AI demonstrates a practical approach to making AI-powered cybersecurity more **explainable, auditable, accountable, controllable, and honest about uncertainty**. **TrustShield AI: The trust and accountability layer for AI-powered cybersecurity.**
10 Aug 2026

AutoPenAI — Autonomous Penetration Testing Agent
Summary Modern security teams cannot keep up with expanding corporate network targets. Traditional human security testing only gives a single snapshot in time and fails to match fast software updates. This autonomous agent solves the problem by continuously scanning, mapping, and testing network defense barriers. Moving through a closed loop from discovery to reporting, the system uses machine learning alongside traditional hacking tools to find open routes, map connections, filter out fake alerts, and safely test threats inside an isolated sandbox. It converts chaotic, raw threat data into clear instructions, moving companies from slow defense reactions to continuous, proactive protection against hackers.
19 May 2026


