
Hussnain Dawood@HussnainDawood
8
Events attended
2
Submissions made
Pakistan
2+ years of experience
About me
Software Engineering student and Full Stack Developer focused on AI-powered applications. I work with Python, MERN, LLMs, LangChain, REST APIs, and machine learning. I enjoy turning ideas into working products and solving real-world problems through AI and modern software engineering. Experienced through internships, hackathons, product-building programs, and hands-on projects.
🤝 Top Collaborators


🤓 Latest Submissions
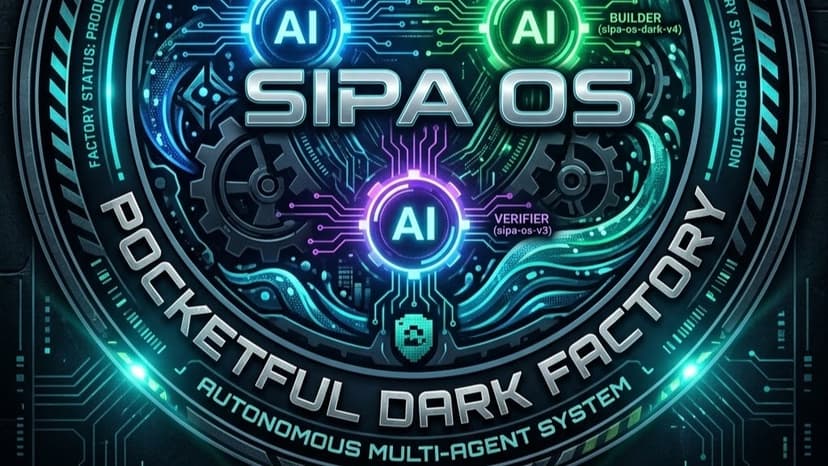
SIPA OS: Pocketful Dark Factory
SIPA OS — Dark Factory is an autonomous multi-agent software engineering system designed to architect, implement, and rigorously verify production-grade microservices without human intervention during development. For the WeAreDevelopers x BAND Dark Factory Hackathon, our team (Aelin AquaSoul) deployed this factory against the Pocketful track to build a secure, high-concurrency financial wallet and payment processing service. Multi-Agent Architecture: The factory operates via three specialized, non-overlapping seats governed by strict system mandates: sipa-os-core (Planner/Architect): Analyzes project specifications, breaks down requirements into sequential work items with explicit done criteria, and coordinates task distribution. sipa-os-dark-v4 (Builder/Implementer): Implements code using the exact mandated tech stack and executes baseline checks. sipa-os-v3 (Verifier/Reviewer): Independently runs container builds and executes rigorous security and invariant attack suites without trusting builder claims. Technical & Security Highlights: Thread-Safe In-Memory Storage: Custom state management backed entirely by Python dictionaries guarded by threading.Lock(). Strict Balance Invariants (I1 & I2): Enforces money conservation (sum of balances always equals the seeded total) and prohibits negative balances/overdrafts, returning a 422 error on violations. Cryptographic Security: Secure password hashing using pre-hashed SHA-256 wrapped into salted bcrypt digests to prevent silent 72-byte truncation vulnerabilities. Idempotency & Validation: User-scoped idempotency keys across all mutating financial endpoints and strict regex-based handle derivation (^[a-z0-9_]{1,20}$). Dockerized Containerization: Fully containerized with dynamic $PORT support and verified using automated pre-flight testing harnesses.
6 Oct 2026
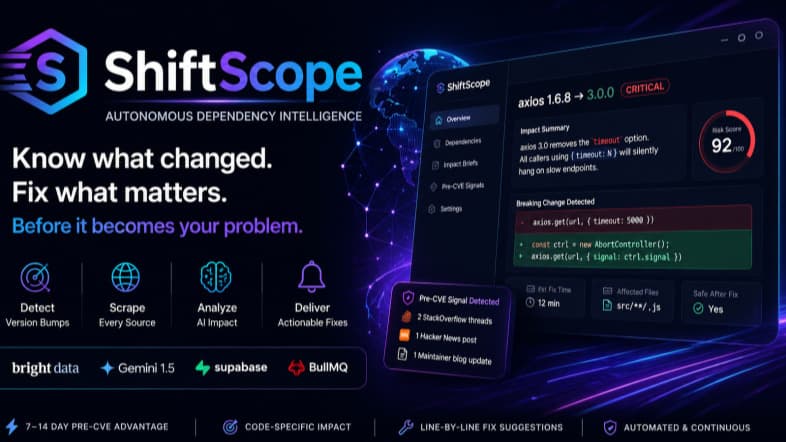
ShiftScope: AI-Powered Dependency Intelligence
ShiftScope is an autonomous dependency intelligence agent that tells you exactly what a package update means for your code — not just that it happened. While tools like Dependabot and Renovate detect version bumps and open PRs, ShiftScope goes further: it scrapes the full human-written context around every release — changelogs, GitHub issues, security blogs, Reddit threads, StackOverflow workarounds — then runs a 5-step AI analysis chain to produce a ranked, code-specific impact brief with line-by-line fix suggestions. It also monitors the pre-CVE window: the 7–14 day gap between public security disclosure and official CVE assignment, during which every standard scanner reports zero vulnerabilities. How it works: A 15-minute cron cycle detects version changes across all major ecosystems (npm, PyPI, Cargo, Go, RubyGems, Maven). For each change, it scrapes 6 source types via Bright Data, stores raw intelligence in Supabase, runs it through Gemini 1.5 Pro, and delivers a severity-ranked brief to Slack, email, webhook, or dashboard — with before/after code diffs and an estimated fix time.
31 May 2026


