
🤝 Top Collaborators

🤓 Latest Submissions
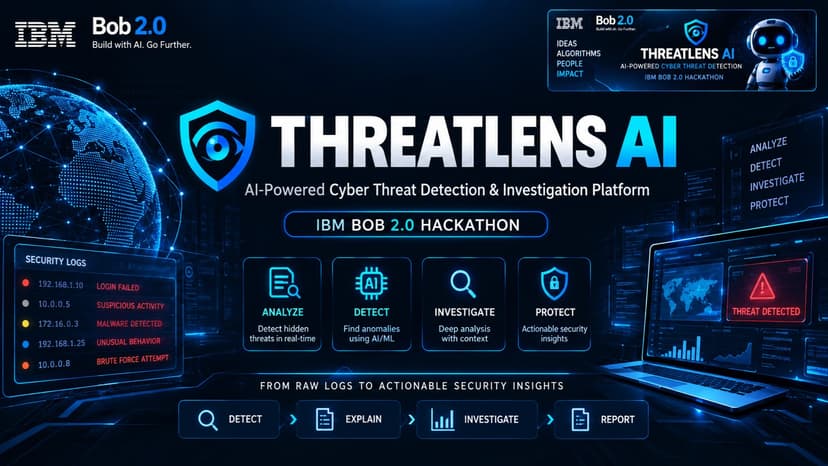
ThreatLens AI
.ThreatLens AI is an AI-powered cybersecurity threat detection and investigation platform designed to transform raw security logs into actionable security insights. Modern servers, networks, and applications continuously generate large volumes of security logs, making it difficult for security teams to manually identify suspicious behavior and hidden attack patterns. ThreatLens AI addresses this challenge by providing an end-to-end workflow for security log analysis, anomaly detection, threat classification, risk assessment, investigation, and reporting. The platform accepts security data from multiple sources and formats, including CSV, JSON, and TXT logs. The data passes through ingestion, validation, cleaning, feature extraction, and scaling before being analyzed by AI/ML components. For anomaly detection, the system uses machine-learning techniques including Isolation Forest to identify unusual activity and deviations from normal behavior. Detected anomalies are further evaluated using security rules, threat classification, and a risk engine to determine threat type, risk score, and risk level. ThreatLens AI also provides an investigation layer that analyzes IP and behavioral information, enriches the available context, and presents explainable security insights to help analysts understand why an activity was flagged. The platform brings detection, risk assessment, investigation, and reporting into a centralized workflow. The final application provides a security dashboard, threat history, report generation, and an AI-assisted security workflow. Its primary goal is to reduce manual log analysis, prioritize suspicious activity, improve investigation efficiency, and provide clearer and more actionable cybersecurity insights for security analysts and infrastructure teams.
27 Sep 2026

