Cohere

Cohere provides access to advanced Large Language Models and NLP tools through one easy-to-use API. They provide multiple models such as Generate, Embed, Semantic Search or Classify

Cohere is a Canadian company that specializes in artificial intelligence. Their mission is to help businesses harness the power of AI to improve their operations. Cohere offers a suite of AI-powered tools that can be used to automate tasks, improve customer service, and boost sales. Their products are designed to be easy to use and integrate with existing business systems. The Cohere natural language processing platform makes it easier for developers to build natural language processing models into applications and helps companies infuse natural language processing capabilities into their business using tools like chatbots, without requiring AI expertise of their own.

General
CompanyCohere
Founded2019
Repositoryhttps://github.com/cohere-ai/
DiscordJoin the Cohere channel on Discord

Start building with Cohere

Cohere has an amazing potential and extraordinary potential usage - you can incorporate it into many of your app ideas and it will solve many of the problems you faced perfectly.


Cohere Embed

For ML teams looking to build their own text analysis applications, Embed offers high-performance, accurate embeddings in English and 100+ languages.

You can easily use Cohere Embed for your app, and all necessary APIs, boilerplates, tutorials explaining how to do so and more, you can find on our Cohere Embed tech page.


Cohere Generate

Generate produces unique content for emails, landing pages, product descriptions, and more.

You can easily use Cohere Generate for your app, and all necessary APIs, boilerplates, tutorials explaining how to do so and more, you can find on our Cohere Generate tech page.


Cohere Classify

Classify organizes information for more effective content moderation, analysis, and chatbot experiences.

You can easily use Cohere Classify for your app, and all necessary APIs, boilerplates, tutorials explaining how to do so and more, you can find on our Cohere Classify tech page.


Neural Search provides powerful semantic search capabilities that find text, documents, and articles based on meaning, not just keywords.

You can easily use Cohere Neural Search for your app, and all necessary APIs, boilerplates, tutorials explaining how to do so and more, you can find on our Cohere Neural Search tech page.


Cohere Boilerplates

Kickstart your development with a Cohere based boilerplate. Boilerplates is a great way to headstart when building your next project with Cohere.


Cohere Libraries

A curated list of libraries and technologies to help you build great projects with Cohere.

  • Cohere Node This package provides functionality developed to simplify interfacing with the cohere.ai natural language API. This SDK provides support for both TypeScript and JavaScript Node.js projects.
  • Cohere Go This package provides functionality developed to simplify interfacing with the cohere.ai natural language API in Go.
  • Cohere Python This package provides functionality developed to simplify interfacing with the Cohere API in Python 3.
  • Cohere Ruby This package provides functionality developed to simplify interfacing with the cohere.ai NLP API in Ruby.

Cohere Sandbox

Sandbox is a collection of experimental, open-source GitHub repositories that make building applications using large language models fast and easy with Cohere.


Cohere AI Technologies top builders

Explore the top contributors showcasing the highest number of Cohere AI Technologies app submissions within our community.

Cohere AI Technologies Hackathon projects

Discover innovative solutions crafted with Cohere AI Technologies, developed by our community members during our engaging hackathons.

Multiagent coding assistant

Multiagent coding assistant

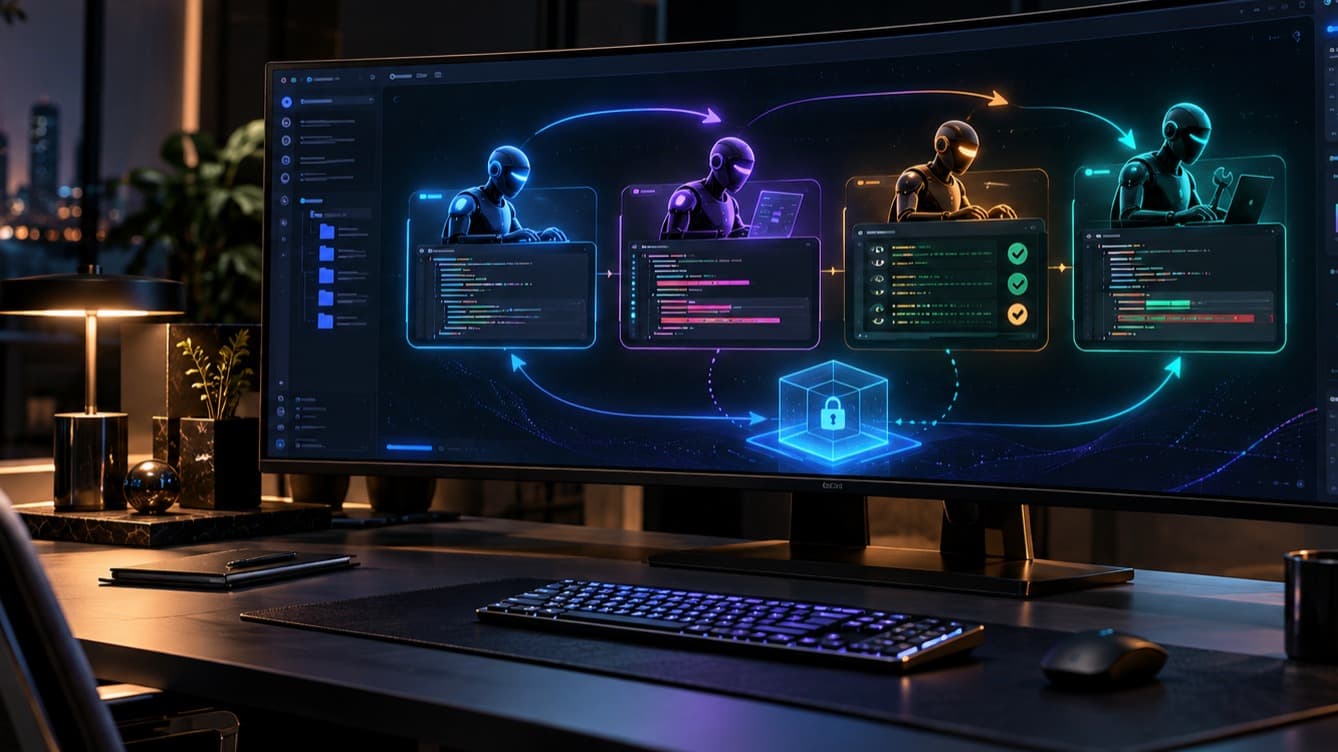
BOB / FORGE is a multi-agent coding assistant designed to make software development safer, faster, and more reliable. Many developers, students, and small teams can generate code quickly, but first drafts often contain hidden bugs, incorrect assumptions, weak input validation, or untested edge cases. Reviewing and testing every generated solution manually is time-consuming, especially for beginners and teams working under tight deadlines. Our solution uses a LangGraph-powered workflow that behaves like an autonomous engineering team. The user enters a natural-language programming request through the web interface. The Builder agent creates an implementation and test contract. The Reviewer agent analyzes the code for logical, structural, and security issues. The Runner executes the tests inside a restricted sandbox, preferably using Docker with network isolation and resource limits. If problems are detected, the Fixer agent applies a targeted correction. The workflow then loops through review and testing until the solution passes or the iteration limit is reached. BOB / FORGE is intended for students, developers, educators, hackathon teams, and anyone who wants an additional layer of confidence before using generated code. Users interact with a simple engineering studio interface that displays the generated artifact, review findings, test output, agent telemetry, iteration count, and final readiness status. What makes the project unique is its “code that argues with itself” approach. Instead of relying on a single code-generation response, the system creates constructive disagreement between specialized agents. It also includes BobRiskNet, a lightweight neural bug-risk model trained on synthetic code-defect patterns. This model provides an additional local risk signal even when no external AI model is configured. By combining generation, adversarial review, sandboxed execution, automated repair, and transparent evidence, BOB / FORGE reduces the chance that users will blindly trust flawed code. It turns code generation from a one-step output into an observable, testable, and repeatable engineering process.

RedSage v2: Human-in-the-Loop Pentest Companion

RedSage v2: Human-in-the-Loop Pentest Companion

RedSage v2 is a local-first, human-in-the-loop penetration-testing and audit workflow companion. It never runs security tooling, launches scans, or automates attacks: the analyst executes every action with their own tools and pastes the output in as evidence. RedSage provides the discipline around that work. New engagements are seeded with a seven-phase PTES-aligned methodology and scoped, non-intrusive audit commands. Operators define in-scope and out-of-scope targets, then lock the scope; every later action is validated against it, and amendments require an authorizer plus rationale, all recorded in an immutable audit log. Pasted evidence runs through a safety pipeline: line clipping, secret redaction (tokens, passwords, JWTs, keys, connection strings), atomic on-disk artifact storage with SHA-256 digests, and redacted excerpts only in the database. An optional AI verifier classifies evidence against the task objective (PASS / FAIL / AMBIGUOUS / CONFIRMED_NEGATIVE) using verbatim grounded quotations and extracted assets, degrading safely to deterministic offline verification when no API key or provider is reachable. Keyword-bearing assets become human-approved task proposals. Confirmed findings require linked verified evidence, and the Report Studio compiles an audit-ready Markdown report: scope attestation, task execution matrix, asset inventory, confirmed findings, and an evidence integrity register. A readiness score flags anything blocking delivery, and projects export to checksummed ZIP archives that re-import with full ID remapping. Built with React and TypeScript on a FastAPI backend over SQLite and ChromaDB, fully local on 127.0.0.1 - AI support for analysis and reporting without surrendering execution control.

RedSage v2: Human-in-the-Loop Pentest Companion

RedSage v2: Human-in-the-Loop Pentest Companion

RedSage v2 is a local-first, human-in-the-loop penetration-testing and audit workflow companion. It never runs security tooling, launches scans, or automates attacks: the analyst executes every action with their own tools and pastes the output in as evidence. RedSage provides the discipline around that work. New engagements are seeded with a seven-phase PTES-aligned methodology and scoped, non-intrusive audit commands. Operators define in-scope and out-of-scope targets, then lock the scope; every later action is validated against it, and amendments require an authorizer plus rationale, all recorded in an immutable audit log. Pasted evidence runs through a safety pipeline: line clipping, secret redaction (tokens, passwords, JWTs, keys, connection strings), atomic on-disk artifact storage with SHA-256 digests, and redacted excerpts only in the database. An optional AI verifier classifies evidence against the task objective (PASS / FAIL / AMBIGUOUS / CONFIRMED_NEGATIVE) using verbatim grounded quotations and extracted assets, degrading safely to deterministic offline verification when no API key or provider is reachable. Keyword-bearing assets become human-approved task proposals. Confirmed findings require linked verified evidence, and the Report Studio compiles an audit-ready Markdown report: scope attestation, task execution matrix, asset inventory, confirmed findings, and an evidence integrity register. A readiness score flags anything blocking delivery, and projects export to checksummed ZIP archives that re-import with full ID remapping. Built with React and TypeScript on a FastAPI backend over SQLite and ChromaDB, fully local on 127.0.0.1 - AI support for analysis and reporting without surrendering execution control.

RedSage v2: Human-in-the-Loop Pentest Companion

RedSage v2: Human-in-the-Loop Pentest Companion

RedSage v2 is a local-first, human-in-the-loop penetration-testing and audit workflow companion. It never runs security tooling, launches scans, or automates attacks: the analyst executes every action with their own tools and pastes the output in as evidence. RedSage provides the discipline around that work. New engagements are seeded with a seven-phase PTES-aligned methodology and scoped, non-intrusive audit commands. Operators define in-scope and out-of-scope targets, then lock the scope; every later action is validated against it, and amendments require an authorizer plus rationale, all recorded in an immutable audit log. Pasted evidence runs through a safety pipeline: line clipping, secret redaction (tokens, passwords, JWTs, keys, connection strings), atomic on-disk artifact storage with SHA-256 digests, and redacted excerpts only in the database. An optional AI verifier classifies evidence against the task objective (PASS / FAIL / AMBIGUOUS / CONFIRMED_NEGATIVE) using verbatim grounded quotations and extracted assets, degrading safely to deterministic offline verification when no API key or provider is reachable. Keyword-bearing assets become human-approved task proposals. Confirmed findings require linked verified evidence, and the Report Studio compiles an audit-ready Markdown report: scope attestation, task execution matrix, asset inventory, confirmed findings, and an evidence integrity register. A readiness score flags anything blocking delivery, and projects export to checksummed ZIP archives that re-import with full ID remapping. Built with React and TypeScript on a FastAPI backend over SQLite and ChromaDB, fully local on 127.0.0.1 - AI support for analysis and reporting without surrendering execution control.